Security and Compliance After 2027: What Losing SAP Patches Really Means
An unsupported ERP system doesn't fail on day one. It degrades quietly, in ways that show up first in an audit finding or a missed tax update — and Canadian finance and compliance teams are already flagging it.
Security and Compliance After 2027: What
Losing SAP Patches Really Means
Losing SAP Patches Really Means
An unsupported ERP system doesn't fail on day one. It degrades quietly, in ways that show up first in an audit finding or a missed tax update — and Canadian finance and
compliance teams are already flagging it.
compliance teams are already flagging it.
There's a comforting myth that circulates in IT departments running older ECC systems: “it still works fine, so what's the actual risk?” RSM, the professional services network with a dedicated Canadian practice, addressed that question directly in a client note aimed at middle-market
executives: once SAP's maintenance ends, organizations lose access to security patches,
compliance updates and vendor-delivered fixes — and the implications of that loss are, in RSM's words, vast.
executives: once SAP's maintenance ends, organizations lose access to security patches,
compliance updates and vendor-delivered fixes — and the implications of that loss are, in RSM's words, vast.
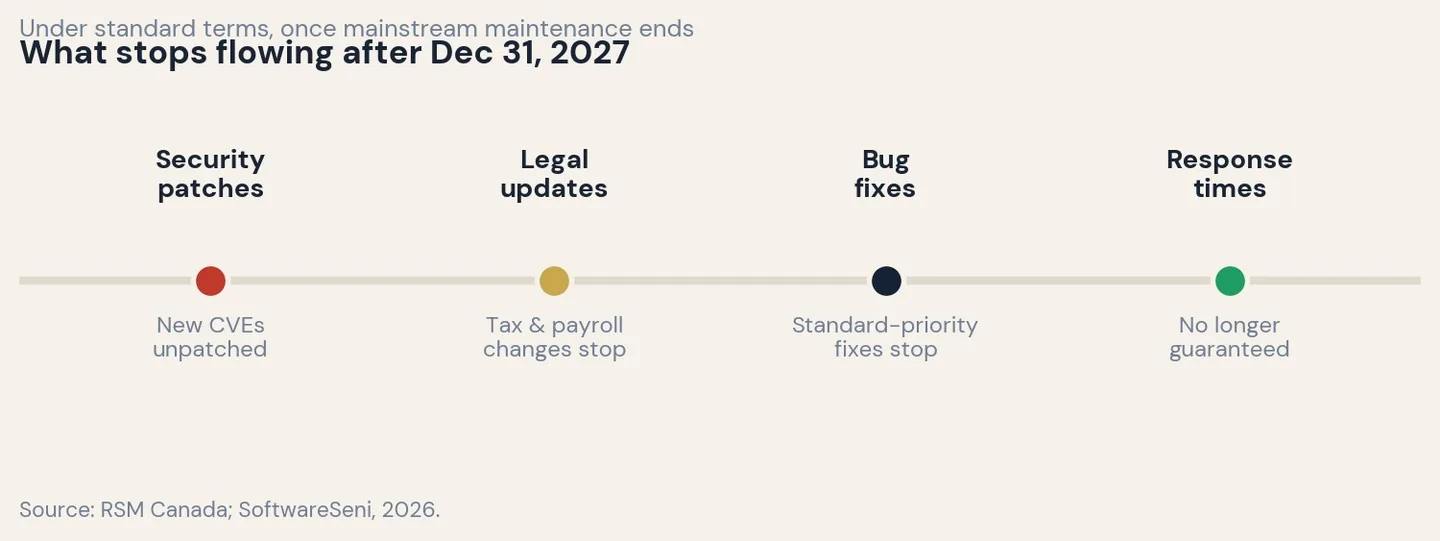
It is worth being specific about what actually stops flowing. Legal change packages — the updates that keep tax tables, payroll rules and statutory reporting current as regulations shift
— are one casualty. So are security patches for vulnerabilities discovered after the
maintenance window closes. New CVEs (the industry's standard way of cataloguing software
vulnerabilities) found in ECC after December 2027 will simply not receive an SAP-issued fix under standard terms. The system keeps functioning exactly as before; what changes is that
nobody is watching for new problems and shipping a fix when one appears.
© Orpington Technologies Inc.
www.orpingtontech.com
Page
1
of
3
— are one casualty. So are security patches for vulnerabilities discovered after the
maintenance window closes. New CVEs (the industry's standard way of cataloguing software
vulnerabilities) found in ECC after December 2027 will simply not receive an SAP-issued fix under standard terms. The system keeps functioning exactly as before; what changes is that
nobody is watching for new problems and shipping a fix when one appears.
This is a gradual degradation, not a cliff edge, and that gradualness is precisely why it is dangerous. Nothing breaks on January 1, 2028. What accumulates instead, quarter over quarter,
is a widening gap between what your ERP system can defend against and what a live vendor-supported system down the street can defend against. Compliance risk compounds in the same way — tax law and regulatory reporting requirements do not freeze just because your ERP support has, and an unpatched system's ability to keep pace with those changes falls further behind every filing period.
is a widening gap between what your ERP system can defend against and what a live vendor-supported system down the street can defend against. Compliance risk compounds in the same way — tax law and regulatory reporting requirements do not freeze just because your ERP support has, and an unpatched system's ability to keep pace with those changes falls further behind every filing period.
For Canadian finance and compliance functions specifically, this lands in a familiar place: audit exposure. An auditor reviewing internal controls over an ERP system running without vendor
security or legal updates is going to ask pointed questions about compensating controls, and
“we have a plan to migrate eventually” is a materially weaker answer than “we are already migrating on a scheduled timeline.” Reputational and regulatory exposure from a control failure tends to be far more expensive, and far more visible, than the migration project that would have prevented it.
security or legal updates is going to ask pointed questions about compensating controls, and
“we have a plan to migrate eventually” is a materially weaker answer than “we are already migrating on a scheduled timeline.” Reputational and regulatory exposure from a control failure tends to be far more expensive, and far more visible, than the migration project that would have prevented it.
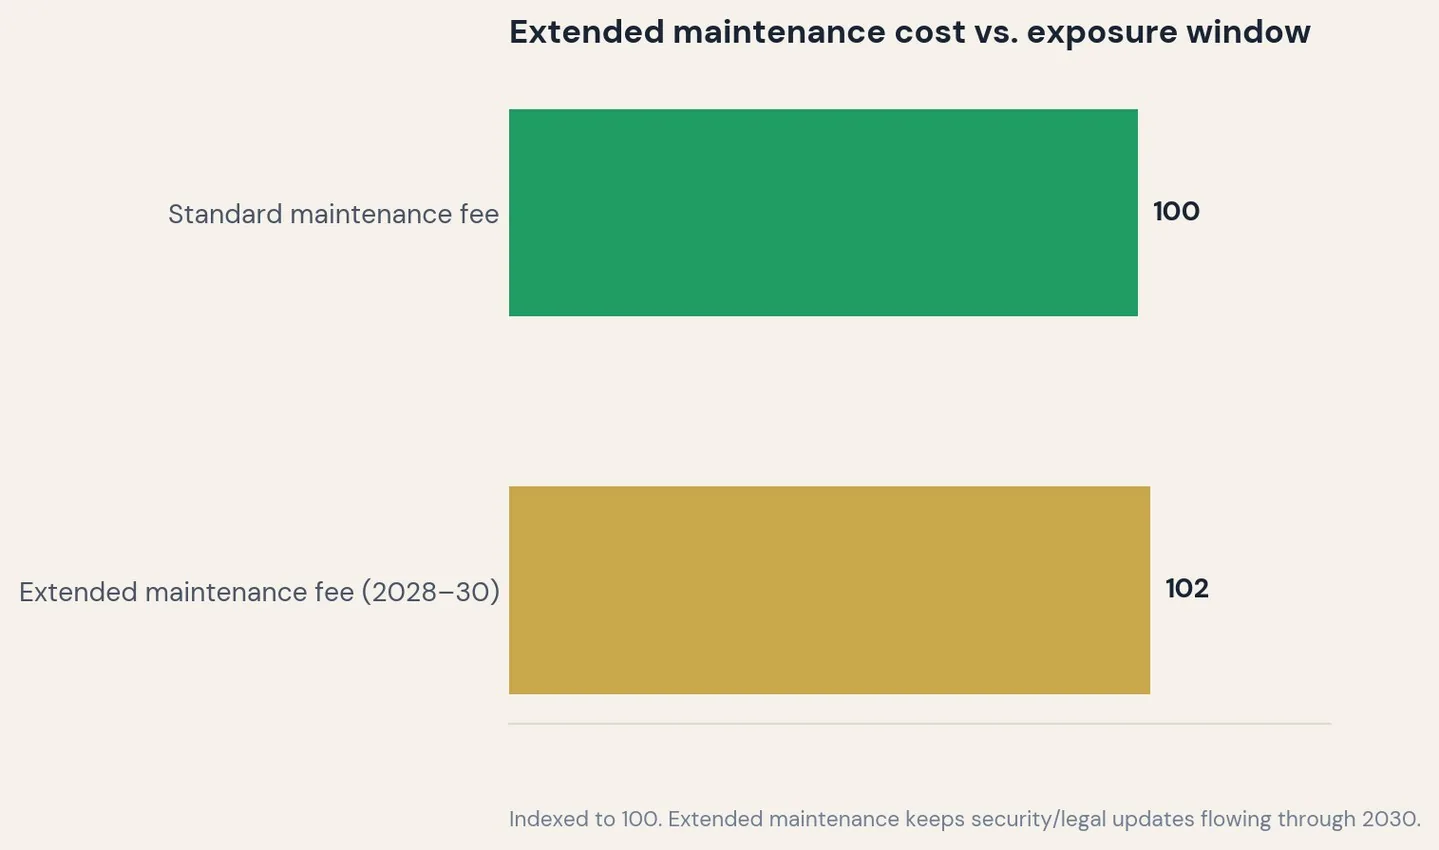
Extended maintenance, available through 2030 for enhancement packages 6 through 8, does
buy real time — it keeps security patches and legal updates flowing at a roughly 2% premium
on existing fees. But it is a bridge with a hard endpoint. Customer-specific maintenance, the tier everyone eventually lands in without a further agreement, provides essentially none of that: no new security patches, no new legal or regulatory updates, and no guaranteed response times, at the same cost as full support.
© Orpington Technologies Inc.
www.orpingtontech.com
Page
2
of
3
buy real time — it keeps security patches and legal updates flowing at a roughly 2% premium
on existing fees. But it is a bridge with a hard endpoint. Customer-specific maintenance, the tier everyone eventually lands in without a further agreement, provides essentially none of that: no new security patches, no new legal or regulatory updates, and no guaranteed response times, at the same cost as full support.
Orpington Technologies | SAP S/4HANA Migration Insights
None of this needs to become a crisis for a Canadian organization with time to plan. It becomes
one for organizations that treat the 2027 deadline as an IT scheduling problem rather than a
governance and risk issue that finance, legal and the audit committee should all have visibility into well before the maintenance window actually closes.
one for organizations that treat the 2027 deadline as an IT scheduling problem rather than a
governance and risk issue that finance, legal and the audit committee should all have visibility into well before the maintenance window actually closes.
This is the framing Orpington Technologies Inc. tends to bring into early client conversations — the Canadian advisory firm treats the security and compliance exposure of staying on
unsupported ECC as a board-level risk item, not a footnote in an IT roadmap, when it helps
organizations build the case for starting migration planning now.
unsupported ECC as a board-level risk item, not a footnote in an IT roadmap, when it helps
organizations build the case for starting migration planning now.
The patches you lose in 2028 are invisible until the moment you need one that never arrives.
Planning around that now costs far less than explaining it to an auditor later.
What stops after mainstream maintenance ends
Category
Status after Dec 31, 2027 (standard terms)
Planning around that now costs far less than explaining it to an auditor later.
New security patches for newly discovered
vulnerabilities
Not provided
vulnerabilities
Legal / regulatory change packages (tax, payroll,
reporting)
Not provided
Standard-priority bug fixes
Not provided
Guaranteed support response times
Not guaranteed
System continues to run
Yes — no immediate functional change
Sources & Further Reading
[1]
RSM Canada – “SAP ECC end of life: What leaders need to know”
[2]
SoftwareSeni – “What SAP ECC End of Support Actually Means and Why 17,000 Companies
Are Not Ready,” March 2026
© Orpington Technologies Inc.
www.orpingtontech.com
Page
3
of
3
reporting)